Hacker Crew Targets European Fridge Systems in Three-Week Attack Wave
A series of cyber operations targeted retail refrigeration, cryptocurrency exchanges, and emergency apps, prompting UK security chiefs to warn of rising threats from AI-driven tools.
By Nikolai Morales ·
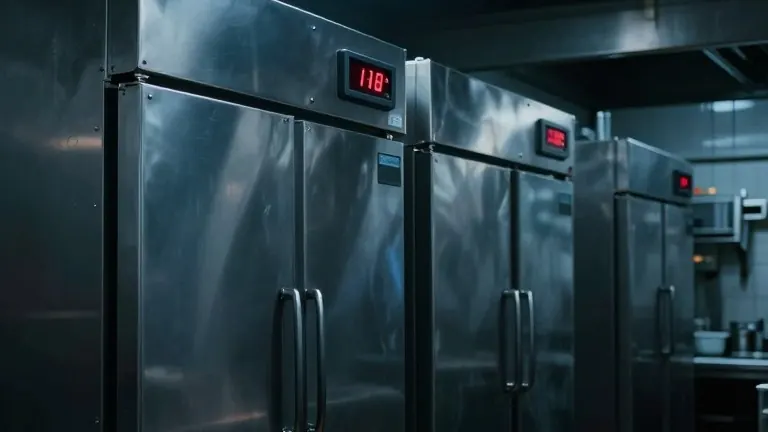
Ax Pearce pulled the internet cable from his refrigeration units on Monday morning after seeing defrost lights flash on at 150C. He suspected a cyber-attack and was correct. On the same day, retailers in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands, and Sweden reported similar issues. Temperatures in some shops reached 50C, threatening stored goods. Pearce, who runs a fruit and vegetable wholesale business in London, noted that a fire could have resulted if he had not been present.
This incident was one of three major attacks over the preceding days. On 30 October, Binance, the largest cryptocurrency exchange, lost $6.3bn in a record heist. On 1 November, hackers sent a fake nuclear strike alert to users of Ukraine’s emergency app in Kyiv. Richard Horne, head of the UK’s National Cyber Security Centre, stated this week that the UK is in the foothills of a new hacking trend. He cited AI technology for exposing flaws in IT systems that were previously hidden.
AI tools are identifying vulnerabilities at a rapid pace. Since April, when Anthropic released its Mythos model, the number of vulnerabilities found by leading tech companies has increased eight-fold. However, Tal Be’ery, a cybersecurity expert, noted that the surge in found flaws has not yet matched the rise in actual breaches. He observed that criminal hackers are currently struggling to profit from these new weaknesses. This is evident in a recent drop in ransomware revenues.
The fridge attacks exploited a specific weakness in commercial refrigeration systems. Hackers targeted companies that provide operating systems for these units. Many of the affected machines were old and no longer received security updates. Danfoss, a Danish firm and one of the affected system providers, stated that most targeted equipment was obsolete. The company said it had long recommended that customers replace or update their software. A key issue is end-of-life products that are no longer maintained.
Geopolitical factors also drive the rise in attacks. Xavier Bellekens, CEO of cybersecurity firm Lupovis, said the fridge attacks bear Russian hallmarks. He noted that the attackers used internet service providers tolerant of malicious activity, a tactic linked to previous Russian operations. The Binance hack has been attributed to North Korea, while Russia is a suspect in the Ukraine alert incident. The UK government launched the Be Ready campaign last month, urging citizens to stock up on food and water in case of emergencies.
Experts in Finland view the recent events as part of a long-standing pattern. The country shares a 1,340km border with Russia and recorded nearly 21,000 cyber incidents last year, up from 13,000 in 2022. Samuli Bergström, vice-president of WithSecure, explained that attackers are mostly opportunistic. He said that any device connected to the internet should be assumed to be attacked eventually. While state actors are sophisticated, a vast economy of independent hackers also contributes to the threat.
The UK’s National Cyber Security Centre expects AI-powered malicious software to target UK power stations, airports, and hospitals by 2028. AI will help attackers scout targets, find weaknesses, and write code. Ollie Whitehouse, the NCSC’s chief technology officer, said manufacturers must invest more in security. He added that consumers need to be willing to pay more for secure products and keep them updated. Pearce now plans to update his fridge monitoring system, which was installed in 2018.
Ciaran Martin, founding chief executive of the NCSC, compared the current situation to previous waves of attacks like NotPetya and WannaCry in 2017. He stated that the current wave is not unprecedented but part of a recurring cycle. He noted that while AI exposes vulnerabilities, the world is not experiencing a unique moment of crisis. The combination of state-sponsored threats and AI tools is creating a higher volume of incidents that require constant vigilance.